BTC $83,162
 ETH $2,506
 USDT $0.9993
 BNB $741.80
 XRP $1.37
 USDC $0.9998
 SOL $107.28
 TRX $0.3275
 FIGR_HELOC $1.05
 ZEC $1,205
Trezor cuts resellers after Ledger uncovers wallet spy implant
The hardware wallet maker is shrinking its authorized reseller network as a precaution following supply-chain attacks.
Key takeaways
- Reseller cutoff date. Trezor reseller authorization ends January 1, 2027, with no new stock shipments allowed.
- Ledger breach scope. Onchain analysts estimate losses from the CryptoBilis breach at $93 million to $103 million.
- Other vendor breaches. Trezor's shipping partner ShipMonk affected 80,689 customers and email provider Brevo exposed 347,000 addresses.
What happened
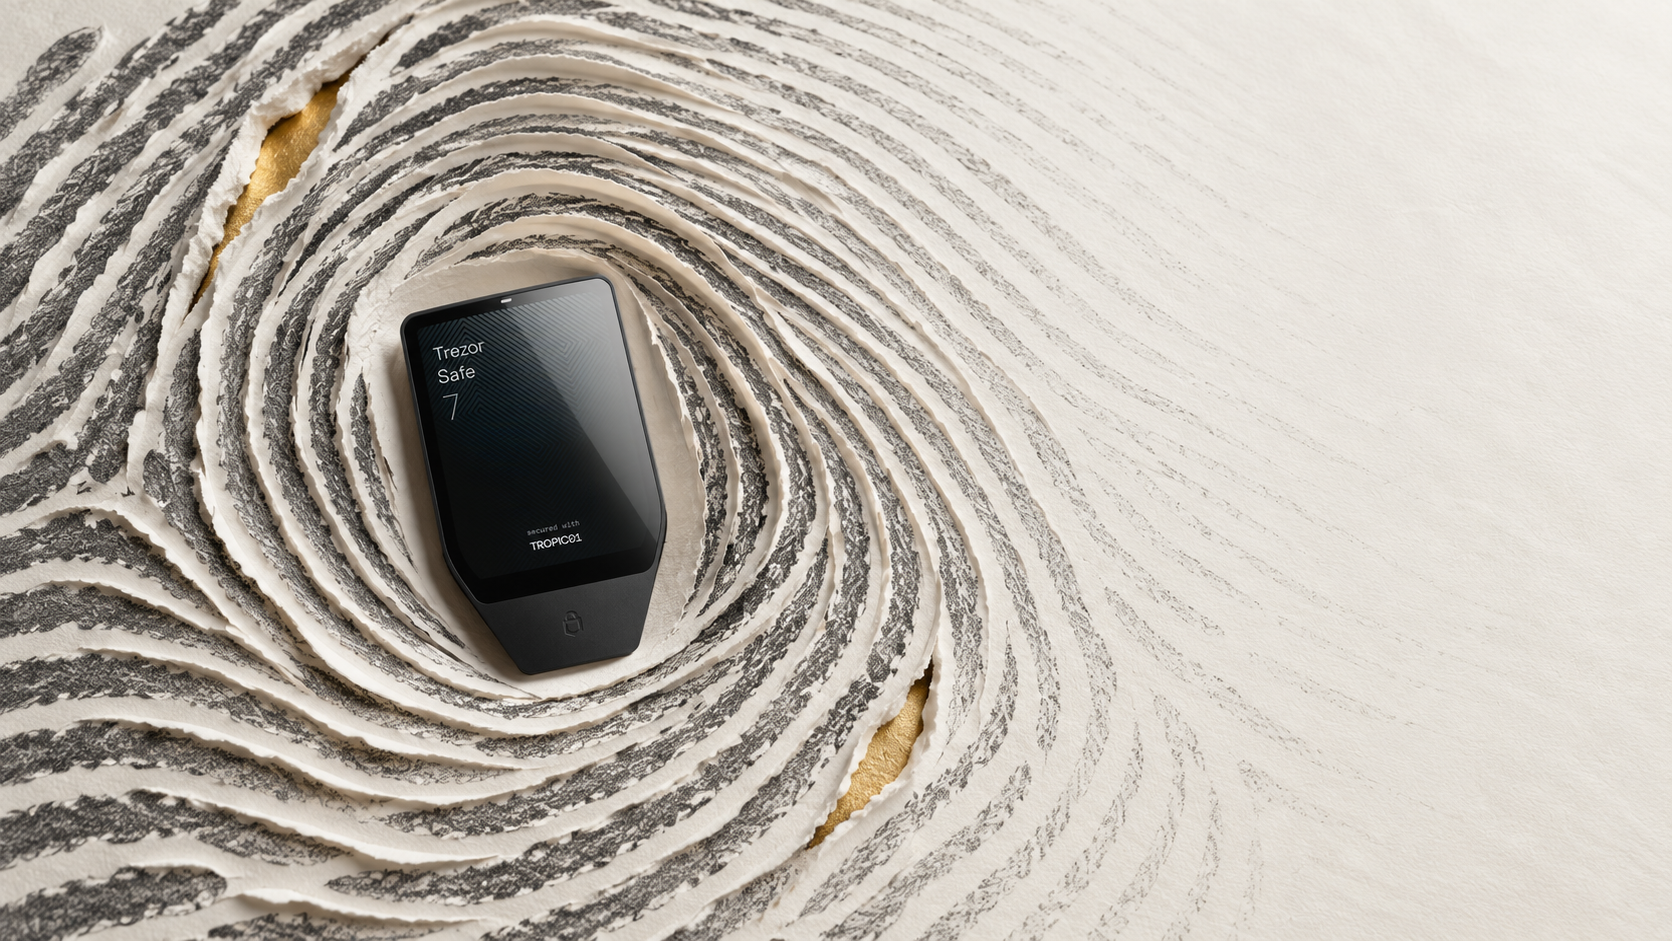
Trezor announced Tuesday it is shrinking its network of authorized resellers, ending partnerships on January 1, 2027. The hardware wallet maker said the move reflects recent supply-chain incidents and lets it more effectively vet the resellers that remain. Trezor stressed that no evidence shows its own devices have been compromised.
The announcement came four days after Ledger confirmed an unauthorized hardware implant in wallets sold through CryptoBilis, a Southeast Asian reseller. The spy component reads the device screen, decodes the recovery phrase when it appears, and sends the words over LTE mobile networks using a built-in eSIM card. Ledger said the implant does not alter the chip storing the keys or the device's operating system, so compromised wallets appear to function normally.
Trezor said CryptoBilis was already off its reseller list and that it had received no reports of tampered Trezor devices from that retailer. The company told resellers being cut that they can continue selling existing inventory through the holiday season but will receive no new stock. Trezor did not disclose how many resellers face removal.
Resellers that keep their authorization will operate under an updated legal framework with stricter rules governing how devices are sourced, stored, and handled. Trezor said it reviewed each country separately, weighing revenue and distribution against the company's direct presence in each market.
Why it matters
Hardware wallets store the secret keys to cryptocurrency offline, protecting them from hackers. Setting up a wallet generates a 24-word recovery phrase that functions as a master password, anyone with those words can empty the wallet from anywhere. If that phrase is intercepted or compromised, the wallet's security is defeated regardless of whether the hardware itself has been altered.
The CryptoBilis breach highlights supply-chain risks that extend beyond the wallet makers themselves. Onchain analysts estimate losses from the compromised devices at between $93 million and $103 million. Trezor has also faced vendor breaches this year: unauthorized access at shipping partner ShipMonk affected 80,689 customers, and a breach at email provider Brevo exposed roughly 347,000 newsletter addresses used in a subsequent phishing campaign.
Questions readers ask
How did the CryptoBilis implant work?
The unauthorized component read the device screen, decoded the recovery phrase when it appeared, and transmitted the words over LTE mobile networks using a built-in eSIM card. The implant did not alter the key storage chip or operating system, so infected devices appeared to work normally.
Were Trezor devices compromised in the CryptoBilis breach?
Trezor said there is not a single piece of evidence that its devices were compromised and received no reports of tampered Trezors sold through CryptoBilis.
When does Trezor's reseller authorization end?
Trezor is ending authorization for resellers on January 1, 2027. Affected resellers can continue selling existing inventory through the holiday season but will receive no new stock.
What other vendor breaches has Trezor experienced?
In August, shipping partner ShipMonk suffered unauthorized access affecting 80,689 customers. In September, email provider Brevo was breached, exposing roughly 347,000 newsletter addresses that attackers used for phishing.