BTC $80,578
 ETH $2,325
 MGLOEURO $111,813
 USDT $0.9991
 BNB $742.92
 XRP $1.28
 USDC $0.9995
 SOL $100.39
 TRX $0.3311
 FIGR_HELOC $1.06
Bitcoin · Explained
Alice & Bob study puts bitcoin key attack within 30,000 qubits
A preprint from the quantum computing firm estimates a fault-tolerant machine could solve bitcoin's elliptic-curve problem in about an hour, though the hardware
Key takeaways
- Smaller than earlier work. Alice & Bob's 2023 estimate for the same elliptic-curve problem was 126,133 cat qubits and nine hours; the new preprint puts the ceiling at 29,588 qubits and 61.8 minutes.
- Timing limits on-spend risk. An hour-long computation still exceeds bitcoin's roughly 10-minute block interval, so the company says ordinary unconfirmed transactions are not the main exposure.
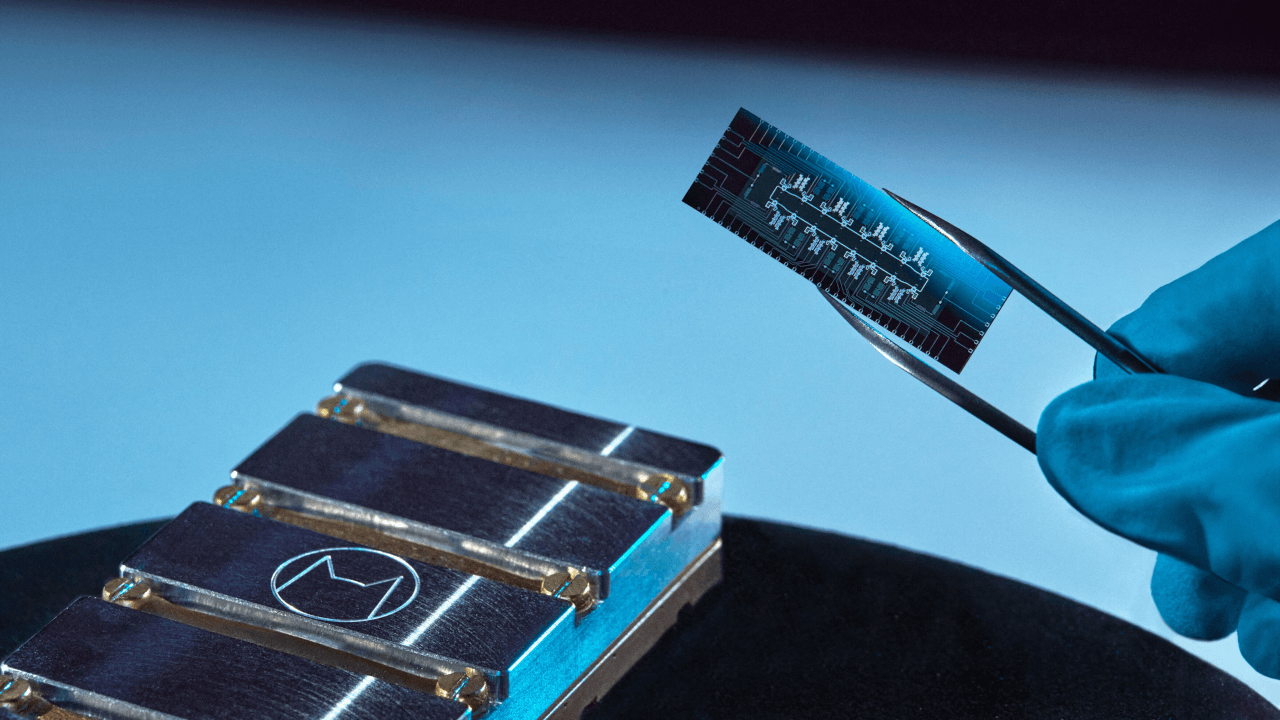
- No hardware yet. The company's most recent published results came from demonstrators no larger than a 12-qubit chip, with logical error rates still above the error-correction threshold.
What happened
Alice & Bob, a quantum computing company with offices in Paris and Boston, said Thursday that a fault-tolerant quantum computer built from about 29,588 of its physical qubits could solve the 256-bit elliptic-curve discrete logarithm problem in 61.8 minutes. That mathematical problem underlies the digital signatures bitcoin uses to prove ownership of funds.
The estimate appeared in a preprint posted to the IACR Cryptology ePrint Archive and targets secp256k1, the specific elliptic curve behind bitcoin signatures. The same paper puts RSA-2048, the encryption widely used across the internet, at 22,593 physical qubits and roughly 3.14 days.
The design depends on cat qubits, a superconducting approach developed by the company that suppresses bit-flip errors in hardware so that error correction only has to handle phase flips. The researchers paired that with more efficient error-correction codes and refinements to the arithmetic that Shor's algorithm requires. Alice & Bob described the output as theoretical resource estimates rather than a demonstration that any existing machine can perform the calculation.
First $84.2KLatest $81K-3.8% over the period
Points are daily observations, not closing prices.
Why it matters
Bitcoin's security model rests on the difficulty of deriving a private key from a public one. A machine capable of that calculation could produce valid signatures without authorization and move coins. Because the estimated hour-long attack takes longer than bitcoin's average 10-minute block interval, the company says transactions waiting for confirmation are relatively sheltered. Coins whose public keys are already visible on the blockchain are a different case, since an attacker would not have to finish the work before the next block.
That distinction has pushed discussion toward preparation. Changing bitcoin's signature system would mean larger transactions, compatibility work across wallets and a way to protect coins in dormant or lost addresses. Alice & Bob joined other voices in urging organizations to adopt post-quantum cryptography before a capable machine exists, arguing that migration takes years.
What the data shows
The projections have fallen sharply over time. In 2019, factoring RSA-2048 was estimated to need about 20 million physical qubits, and a revision from Google Quantum AI last year brought the figure under one million. Alice & Bob's own 2023 research put a 256-bit elliptic-curve logarithm at 126,133 cat qubits and nine hours, against 29,588 qubits and just over an hour now.
CryptoPotato noted that the paper treats its numbers as a ceiling, since the bitcoin calculation reuses circuits compiled for RSA-2048. The figures also assume no bit flips occur during the computation, equivalent to a bit-flip time of about a century. With a bit flip roughly once an hour, the RSA-2048 estimate rises from 22,593 qubits to about 45,000.
For comparison, Google Quantum AI's March whitepaper described a design needing fewer than 500,000 physical qubits that, primed in advance, could recover a single wallet's key in about nine minutes once a public key appeared. CryptoPotato reported that Google counted more than 1.7 million BTC held in Pay-to-Public-Key scripts, an early address type that leaves the public key on-chain. Bitcoin.com News, citing earlier estimates, reported that approximately 6.9 million BTC could face exposure because the corresponding public keys have already been revealed.
Background
The preprint lands after several announcements pointing to gradual technical progress. Google Quantum AI demonstrated a technique called magic state cultivation that improved the reliability of specialized quantum states by a factor of 40, and Quantinuum said on Oct. 19 that its Helios system reached 99.9995% logical fidelity, about five errors per million operations, supporting its ambition to deliver a commercially useful fault-tolerant machine by 2029.
Alice & Bob's own hardware is much smaller. Results published Oct. 20, covering the first phase of PROQCIMA, the French government's quantum program, came from three demonstrators, the largest on a 12-qubit chip, and their logical error rate had not yet dropped below the error-correction threshold. Chief executive Théau Peronnin said in a statement that estimates of the resources needed to run the algorithm have been steadily falling as the field develops better error correction and algorithm design.
What to watch
Alice & Bob expects improving hardware and declining resource requirements to converge in the early 2030s, a projection rather than an established timeline. On the bitcoin side, developers Jameson Lopp and five others have proposed BIP-361, which would freeze quantum-vulnerable legacy addresses in phases. How the network would handle exposed keys, and whether such a proposal could gather consensus, remains unresolved.
Questions readers ask
Does this mean bitcoin can be cracked now?
No. The figures are theoretical resource estimates for a fault-tolerant machine. Alice & Bob's largest published demonstrator sits on a 12-qubit chip and has not yet reached the error-correction threshold.
Which bitcoin coins are most exposed?
Coins whose public keys are already recorded on-chain, such as those in Pay-to-Public-Key addresses, since an attacker would not be racing a 10-minute block confirmation.
What is a cat qubit?
It is Alice & Bob's superconducting qubit design, built to suppress bit-flip errors in hardware so that error correction handles only phase flips, reducing the physical qubits needed per logical qubit.