BTC $64,904
 EQQQQ $655.75 Last updated 8 Nov 2026, 12:03 UTC
 ETH $1,837
 MGLOEURO $111,813
 USDT $0.9993
 BNB $593.99
 USDC $0.9996
 XRP $0.9637
 SOL $72.83
 TRX $0.3060
Hacks & Security · Explained
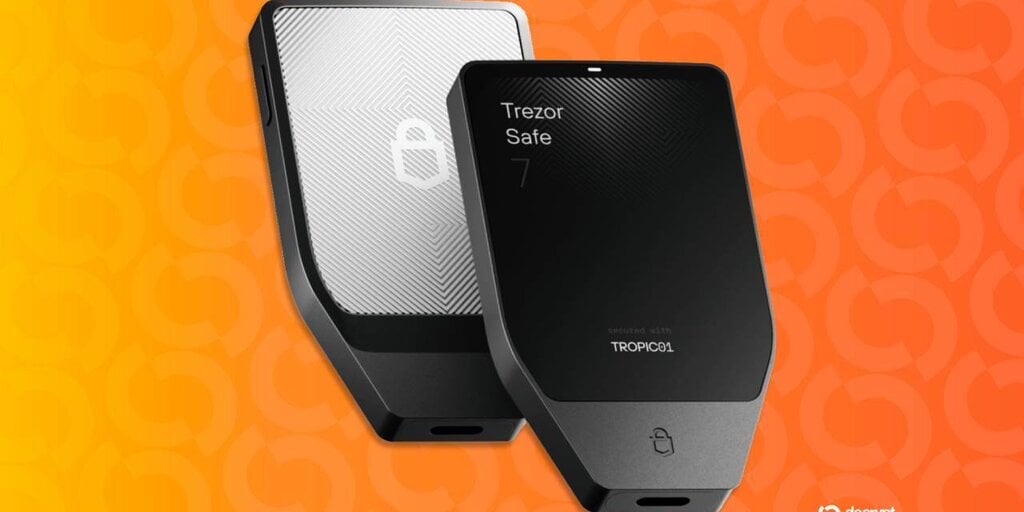
Trezor says shipping partner breach exposed data on 27,000 orders
The bitcoin wallet maker says hackers accessed Skladon's systems and likely exported order records, its third third-party data incident since August.
Key takeaways
- Third incident. Trezor has now disclosed three distinct third-party data incidents in a little over three months, at ShipMonk, at Brevo and now at Skladon.
- No keys involved. Wallet backups, PINs and passphrases were not part of the exposed data, and Trezor says its own infrastructure was untouched.
- Physical risk. A name, a home address and proof of a hardware wallet purchase together can make scams aimed at crypto holders far more convincing.
What happened
Trezor has disclosed that an attacker reached systems operated by Skladon, one of the logistics partners that ships its hardware wallets, and appears to have exported order information covering roughly 27,000 purchases. In a notice published Monday, the bitcoin wallet manufacturer said its own systems were untouched and that customers' devices remain secure. The intrusion at Skladon is said to have occurred on Nov. 7.
According to the disclosure, Skladon did not inform Trezor of the incident until Nov. 15. The records involved relate to orders placed between Aug. 9 and Nov. 7 and include full names, phone numbers, delivery addresses, email addresses, the products bought and the prices paid. Trezor said no wallet backups, PINs or passphrases formed part of the data.
Because Skladon does not handle deliveries to the United States, American buyers were not caught up in this incident, the company said. Trezor has contacted affected customers where it could, although some people who ordered between Aug. 9 and Aug. 14 may not receive a message because their records had already been anonymised.
First $82KLatest $64.9K-20.8% over the period
Points are daily observations, not closing prices.
Why it matters
The exposed fields do not by themselves give anyone the ability to move a customer's coins, but together they pair a home address with evidence that the resident owns cryptocurrency hardware. Cointelegraph noted that a leaked shipping record of this kind links a person to an address and to the fact that they hold crypto, which is why the fallout can go beyond unwanted email. Trezor said some customers have already reported fraudulent phone calls. A caller who can name the exact model and price of a device, or a letter sent to a genuine address, can make a phishing approach look authentic. Trezor's guidance on X was to treat any unexpected call, text, email or letter about an order as suspicious, adding that the company never cold-calls customers or asks for a wallet backup.
What the data shows
The current incident covers about 27,000 orders shipped through Skladon between Aug. 9 and Nov. 7. It follows an August breach at logistics provider ShipMonk that initially appeared to affect fewer than 14,000 customers, later revised to about 13,700 by Cointelegraph, before a wider investigation found records for another roughly 67,000 US buyers from 2019 to 2021 that the company had retained despite assurances they had been deleted, taking the total to 80,689 people. In September, an incident at marketing email provider Brevo led to the export of 347,149 addresses, which were then used to send a fake security warning through Trezor's legitimate channel. Earlier episodes include a 2022 Mailchimp insider attack and a 2024 breach of an external support portal that put the contact details of as many as 66,000 people at risk. Trezor says it is working to cut order-data retention from 90 days to 45 and will require shipping partners to follow the same policy.
Background
This is not Trezor's first encounter with leaked customer information, and the company has argued that outsourcing part of its operations is a practical necessity. Responding to a question on X about why an order from its official store involved an outside firm, Trezor said companies of its size and global reach cannot run efficiently without third-party service providers, describing the matter as a logistics rather than a technical question. It said Skladon held only the data needed to deliver parcels. The consequences of earlier leaks have included physical-world scams: in February, letters bearing Trezor branding, holograms and QR codes pointing to phishing sites were mailed to hardware-wallet owners. As a partial remedy, Trezor has introduced anonymous pickup at parcel lockers or collection points in 18 European countries, letting buyers order without supplying a home address.
What to watch
Trezor has notified a data protection authority but has not said which one, and it has not explained how attackers gained access to Skladon's systems. How the shortened 45-day retention window and the new partner requirements are enforced will matter for future incidents, as will the speed with which logistics providers report intrusions, given the eight-day gap between the Skladon breach and Trezor's notification. Customers should also expect follow-up phishing attempts that cite real order details.
Questions readers ask
Were my wallet or funds compromised?
Trezor says its own systems were not breached and that no wallet backups, PINs or passphrases were exposed, so the incident alone does not allow anyone to move a customer's coins. What was exposed is order data held by the shipping partner Skladon.
Which customers are affected?
The data covers roughly 27,000 orders placed between Aug. 9 and Nov. 7 and shipped through Skladon, which does not deliver to the United States, so US buyers are unaffected. Some customers who ordered between Aug. 9 and Aug. 14 may not get an email because their records were already anonymised.
What is Trezor changing?
The company is offering anonymous pickup at parcel lockers and collection points in 18 European countries, plans to reduce order-data retention from 90 days to 45, and says shipping partners will have to meet the same standard.